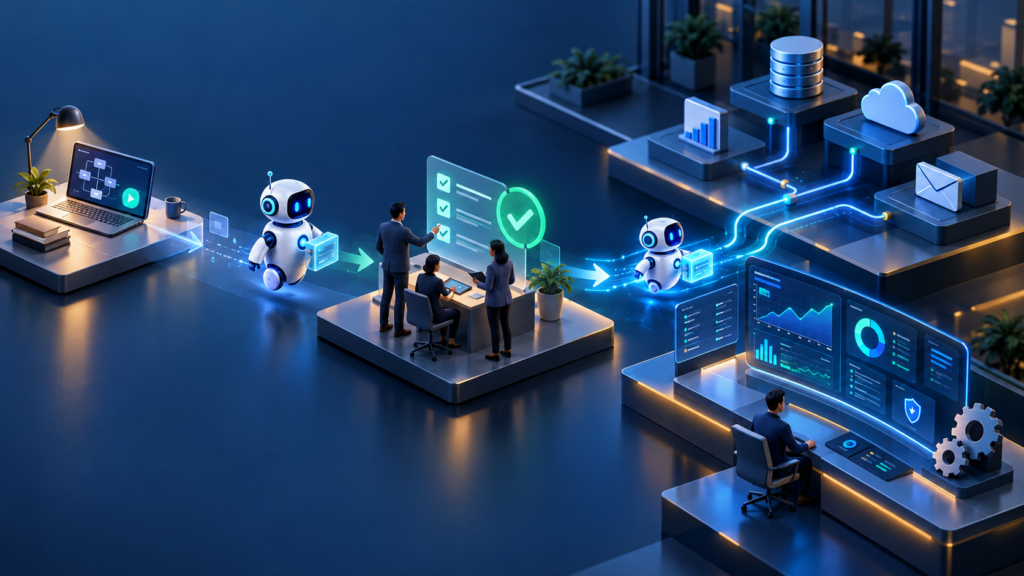

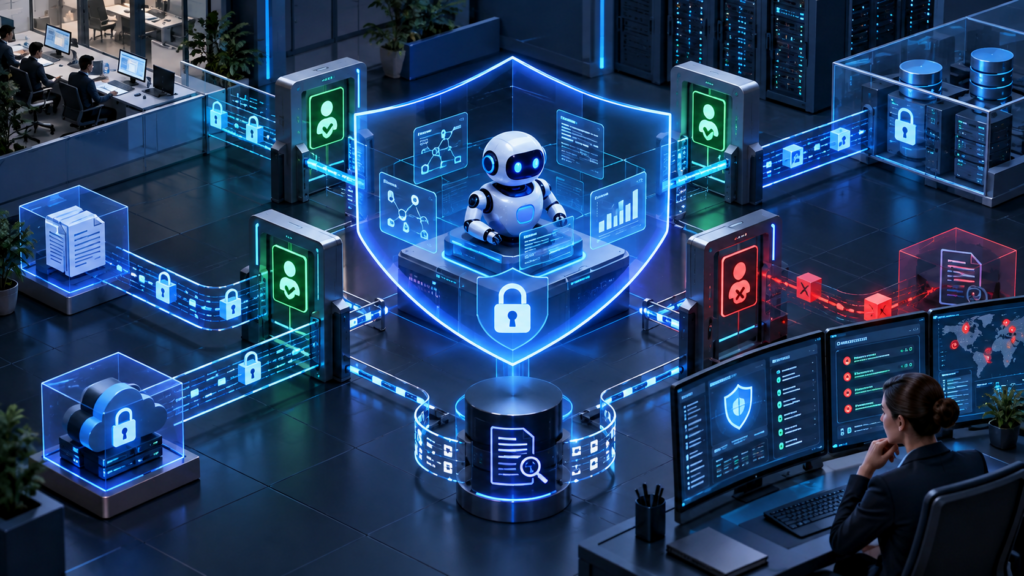
AI agents are different from ordinary chat interfaces because they can retrieve information, call tools, and take actions. That capability creates value, but it also creates a larger security boundary. Before deploying an agent, businesses should know exactly what it can see, what it can do, and how those actions are recorded.
1. Define the agent’s identity and permissions
Give every agent its own identity and least-privilege permissions. Avoid sharing a broad administrator credential across tools. Separate read access from write access, and require a stronger approval path for actions that are financial, legal, customer-facing, or difficult to reverse.
2. Protect sensitive data
Classify the data the agent may access and keep sensitive information out of prompts unless it is required. Apply tenant isolation, encryption, retention limits, and redaction for personal or confidential data. Review whether data is sent to external model providers and understand the provider’s retention terms.
3. Treat retrieved content as untrusted input
Documents, web pages, tickets, and emails can contain instructions designed to manipulate an agent. Retrieval should provide context, not authority. Keep system policies separate from retrieved content, validate tool arguments, and test for prompt injection and data-exfiltration scenarios.
4. Secure tools, APIs, and agent protocols
Tool definitions should be explicit and narrow. Validate inputs on the server, enforce authorization again at the API boundary, and log the user, agent, tool, parameters, and result. For agent protocols such as MCP, maintain an inventory of servers and tools and review changes before they enter production.
5. Add monitoring and an incident plan
Monitor unusual tool calls, repeated failures, permission errors, unexpected data volume, and changes in behavior. Define how to revoke credentials, disable an agent, preserve logs, notify stakeholders, and recover affected data. A kill switch is a basic production requirement.
6. Test the complete workflow
- Can the agent access another user’s data?
- Can a malicious document change its behavior?
- Can it perform an irreversible action without approval?
- What happens when a tool returns an error?
- Can the team explain why a decision was made?
Security is part of the product
Security cannot be added after an agent has been connected to every business system. Start with a narrow scope, create a written permission model, test realistic abuse cases, and expand only when the controls are working. Responsible AI delivery is ultimately a combination of application security, data governance, and operational discipline.
Put these ideas into practice
Explore where AI could help your business.
Discuss your workflow, available data, and the result you want before deciding what to build.